LEA-RECT: A Parallel Hybrid Lightweight Block Cipher Combining ARX Diffusion and Bit-Slice S-Box Nonlinearity for Big-Data-At-Rest Encryption
DOI:
https://doi.org/10.29304/jqcsm.2026.18.33189Keywords:
lightweight cryptography, hybrid block cipher, LEA, RECTANGLE, ARX, bit-slice S-box, big data, HDFS,Abstract
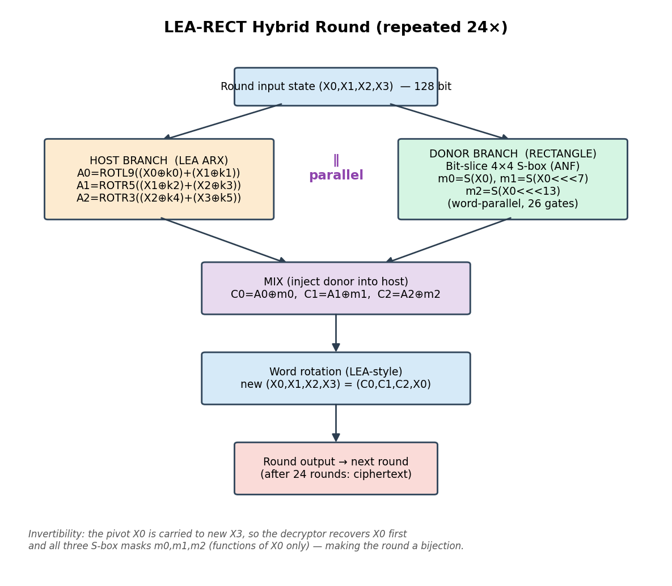
The rapid growth of big-data platforms such as Hadoop/HDFS has intensified the need to protect very large volumes of data at rest without imposing the heavy cost of conventional block ciphers. Purely ARX-based lightweight ciphers (e.g., LEA) achieve fast word-level diffusion but contain no substitution box, and therefore rely solely on modular addition for nonlinearity; purely substitution-permutation ciphers (e.g., RECTANGLE) provide strong algebraic nonlinearity through a bit-slice S-box but are comparatively slower for wide-word software encryption. This paper proposes LEA-RECT, a hybrid lightweight block cipher in which the most important component of a donor cipher (the RECTANGLE bit-slice 4×4 S-box) is embedded, in parallel, alongside the most important component of a host cipher (the LEA ARX round function), and the two branches are then mixed within every round. The construction operates on 128-bit blocks with a 128-bit key over 24 rounds, and is designed so that each round remains a bijection despite the parallel S-box injection. A complete reference implementation was built and validated: encryption/decryption round-trip correctness was confirmed over 30,000 random trials; the cipher attains a mean strict-avalanche of 50.05% for plaintext-bit changes and 50.02% for key-bit changes; ciphertext byte entropy of 7.9998 bits/byte; and it passes the NIST monobit (p=0.96), runs (p=0.96), and block-frequency (p=0.20) randomness tests. The parallel donor branch adds algebraic nonlinearity absent from the ARX host at a measured serial overhead of ~128% on our single-threaded reference implementation; based on the branches’ data-independence, the parallel overhead reduced by simulation to ~32% under 4-way SIMD comparing with serial algorithm, and pending hardware validation.
Downloads
References
D. Hong, J.-K. Lee, D.-C. Kim, D. Kwon, K. H. Ryu, and D.-G. Lee, "LEA: A 128-bit block cipher for fast encryption on common processors," in Information Security Applications (WISA 2013), LNCS, vol. 8267, Cham, Switzerland: Springer, 2014, pp. 3–27. doi: 10.1007/978-3-319-05149-9_1. [Online]. Available: https://doi.org/10.1007/978-3-319-05149-9_1
W. Zhang, Z. Bao, D. Lin, V. Rijmen, B. Yang, and I. Verbauwhede, "RECTANGLE: a bit-slice lightweight block cipher suitable for multiple platforms," Science China Information Sciences, vol. 58, no. 12, pp. 1–15, 2015. doi: 10.1007/s11432-015-5459-7. [Online]. Available: https://doi.org/10.1007/s11432-015-5459-7
H. A. Mohammed and A. K. Farhan, "PRC6: Hybrid lightweight cipher for enhanced cloud data security in parallel environment," Security and Privacy, vol. 7, no. 5, e413, 2024. doi: 10.1002/spy2.413. [Online]. Available: https://doi.org/10.1002/spy2.413
J. R. Naif, I. S. Ahmed, N. D. Zaki, and H. K. Hoomod, "EAMSA 512: new 512-bit encryption algorithm based on modified SALSA20," Iraqi Journal of Computer Science and Mathematics, vol. 4, no. 2, pp. 131–142, 2023. doi: 10.52866/ijcsm.2023.02.02.011. [Online]. Available: https://doi.org/10.52866/ijcsm.2023.02.02.011
R. Beaulieu, D. Shors, J. Smith, S. Treatman-Clark, B. Weeks, and L. Wingers, "The SIMON and SPECK families of lightweight block ciphers," Cryptology ePrint Archive, Report 2013/404, 2013. [Online]. Available: https://eprint.iacr.org/2013/404
R. Beaulieu, D. Shors, J. Smith, S. Treatman-Clark, B. Weeks, and L. Wingers, "The SIMON and SPECK lightweight block ciphers," in Proc. 52nd ACM/EDAC/IEEE Design Automation Conference (DAC), 2015, pp. 1–6. doi: 10.1145/2744769.2747946. [Online]. Available: https://doi.org/10.1145/2744769.2747946
A. Bogdanov, L. R. Knudsen, G. Leander, C. Paar, A. Poschmann, M. J. B. Robshaw, Y. Seurin, and C. Vikkelsoe, "PRESENT: an ultra-lightweight block cipher," in Cryptographic Hardware and Embedded Systems (CHES 2007), LNCS, vol. 4727, Springer, 2007, pp. 450–466. doi: 10.1007/978-3-540-74735-2_31. [Online]. Available: https://doi.org/10.1007/978-3-540-74735-2_31
S. Banik, S. K. Pandey, T. Peyrin, Y. Sasaki, S. M. Sim, and Y. Todo, "GIFT: a small present," in Cryptographic Hardware and Embedded Systems (CHES 2017), LNCS, vol. 10529, Springer, 2017, pp. 321–345. doi: 10.1007/978-3-319-66787-4_16. [Online]. Available: https://doi.org/10.1007/978-3-319-66787-4_16
D. J. Bernstein, "ChaCha, a variant of Salsa20," in Workshop Record of SASC 2008: The State of the Art of Stream Ciphers, 2008. [Online]. Available: https://cr.yp.to/chacha/chacha-20080128.pdf
D. J. Bernstein, "The Salsa20 family of stream ciphers," in New Stream Cipher Designs, LNCS, vol. 4986, Springer, 2008, pp. 84–97. doi: 10.1007/978-3-540-68351-3_8. [Online]. Available: https://doi.org/10.1007/978-3-540-68351-3_8
International Organization for Standardization, "Information security — Lightweight cryptography — Part 2: Block ciphers," ISO/IEC 29192-2:2019, 2019. [Online]. Available: https://www.iso.org/standard/78477.html
L. E. Bassham et al., "A statistical test suite for random and pseudorandom number generators for cryptographic applications," NIST Special Publication 800-22 Rev. 1a, National Institute of Standards and Technology, 2010. doi: 10.6028/NIST.SP.800-22r1a. [Online]. Available: https://doi.org/10.6028/NIST.SP.800-22r1a
K. A. McKay, L. Bassham, M. S. Turan, and N. Mouha, "Report on lightweight cryptography," NIST Interagency Report NISTIR 8114, 2017. doi: 10.6028/NIST.IR.8114. [Online]. Available: https://doi.org/10.6028/NIST.IR.8114
M. J. Dworkin, "Recommendation for block cipher modes of operation: methods and techniques," NIST Special Publication 800-38A, 2001. doi: 10.6028/NIST.SP.800-38a. [Online]. Available: https://doi.org/10.6028/NIST.SP.800-38a
J. Daemen and V. Rijmen, The Design of Rijndael: AES — The Advanced Encryption Standard. Berlin, Germany: Springer, 2002. doi: 10.1007/978-3-662-04722-4. [Online]. Available: https://doi.org/10.1007/978-3-662-04722-4
E. Biham and A. Shamir, "Differential cryptanalysis of DES-like cryptosystems," Journal of Cryptology, vol. 4, no. 1, pp. 3–72, 1991. doi: 10.1007/BF00630563. [Online]. Available: https://doi.org/10.1007/BF00630563
M. Matsui, "Linear cryptanalysis method for DES cipher," in Advances in Cryptology (EUROCRYPT 1993), LNCS, vol. 765, Springer, 1994, pp. 386–397. doi: 10.1007/3-540-48285-7_33. [Online]. Available: https://doi.org/10.1007/3-540-48285-7_33
N. Mouha, Q. Wang, D. Gu, and B. Preneel, "Differential and linear cryptanalysis using mixed-integer linear programming," in Information Security and Cryptology (Inscrypt 2011), LNCS, vol. 7537, Springer, 2012, pp. 57–76. doi: 10.1007/978-3-642-34704-7_5. [Online]. Available: https://doi.org/10.1007/978-3-642-34704-7_5
D. Hong et al., "HIGHT: a new block cipher suitable for low-resource device," in Cryptographic Hardware and Embedded Systems (CHES 2006), LNCS, vol. 4249, Springer, 2006, pp. 46–59. doi: 10.1007/11894063_4. [Online]. Available: https://doi.org/10.1007/11894063_4
B. Koo, D. Roh, H. Kim, Y. Jung, D.-G. Lee, and D. Kwon, "CHAM: a family of lightweight block ciphers for resource-constrained devices," in Information Security and Cryptology (ICISC 2017), LNCS, vol. 10779, Springer, 2018, pp. 3–25. doi: 10.1007/978-3-319-78556-1_1. [Online]. Available: https://doi.org/10.1007/978-3-319-78556-1_1
H. Seo et al., "Efficient parallel implementation of CTR mode of ARX-based block ciphers on ARMv8 microcontrollers," Applied Sciences, vol. 11, no. 6, art. 2548, 2021. doi: 10.3390/app11062548. [Online]. Available: https://doi.org/10.3390/app11062548
S. An, S. C. Seo, "Efficient parallel implementations of LWE-based and ARX-based ciphers on GPUs," Mathematics, vol. 8, no. 11, art. 1894, 2020. doi: 10.3390/math8111894. [Online]. Available: https://doi.org/10.3390/math8111894
K. Shim, "A survey of public-key cryptographic primitives in wireless sensor networks," IEEE Communications Surveys & Tutorials, vol. 18, no. 1, pp. 577–601, 2016. doi: 10.1109/COMST.2015.2459691. [Online]. Available: https://doi.org/10.1109/COMST.2015.2459691
X. Lu, Z. Pan, and H. Xian, "An efficient and secure data sharing scheme for mobile devices in cloud computing," Journal of Cloud Computing, vol. 9, art. 60, 2020. doi: 10.1186/s13677-020-00207-5. [Online]. Available: https://doi.org/10.1186/s13677-020-00207-5
P. K. Premkamal, S. K. Pasupuleti, A. K. Singh, and P. J. A. Alphonse, "Enhanced attribute based access control with secure deduplication for big data storage in cloud," Peer-to-Peer Networking and Applications, vol. 14, pp. 102–120, 2021. doi: 10.1007/s12083-020-00940-3. [Online]. Available: https://doi.org/10.1007/s12083-020-00940-3
D. Ding, C. Sun, and J. Zeng, "Fuzzy weighted clustering method for numerical attributes of communication big data based on cloud computing," Symmetry, vol. 12, no. 4, art. 530, 2020. doi: 10.3390/sym12040530. [Online]. Available: https://doi.org/10.3390/sym12040530
P. Rashmi, M. C. Supriya, and Q. Hua, "Enhanced Lorenz-chaotic encryption method for partial medical image encryption and data hiding in big data healthcare," Security and Communication Networks, vol. 2022, art. 9363377, 2022. doi: 10.1155/2022/9363377. [Online]. Available: https://doi.org/10.1155/2022/9363377
C. E. Shannon, "Communication theory of secrecy systems," Bell System Technical Journal, vol. 28, no. 4, pp. 656–715, 1949. doi: 10.1002/j.1538-7305.1949.tb00928.x. [Online]. Available: https://doi.org/10.1002/j.1538-7305.1949.tb00928.x
A. F. Webster and S. E. Tavares, "On the design of S-boxes," in Advances in Cryptology (CRYPTO 1985), LNCS, vol. 218, Springer, 1986, pp. 523–534. doi: 10.1007/3-540-39799-X_41. [Online]. Available: https://doi.org/10.1007/3-540-39799-X_41
Downloads
Published
How to Cite
Issue
Section
License
Copyright (c) 2026 Shakir Fadhil Shabram

This work is licensed under a Creative Commons Attribution-NonCommercial-NoDerivatives 4.0 International License.